Vendor inventory
Keep legal names, services, ownership, data access, systems access, criticality, contacts, and status in one controlled record.
Third-party risk management for financial services
ThirdNexa replaces disconnected spreadsheets and inboxes with an accountable workflow built around the records regulators and examiners expect firms to maintain.
The operational layer
ThirdNexa organizes the work and preserves the evidence. Your firm determines which obligations apply, evaluates each vendor, and records every approval or compliance conclusion.
Keep legal names, services, ownership, data access, systems access, criticality, contacts, and status in one controlled record.
Run initial and recurring reviews with questionnaires, supporting evidence, findings, remediation, recommendations, and recorded firm decisions.
Track agreements, renewal terms, notice windows, evidence expiration dates, and Regulation S-P notice-clause verification.
A dedicated tab on every vendor records customer-information handling, the breach-notice clause and its notification window, written assurances such as SOC 2 reports, and a dated monitoring log — with a firm-level readiness view and per-vendor exam evidence exports.
Record breaches, outages, and cyberattacks with severity, customer-information involvement, root cause, and attachments. Reference timers track the 72-hour vendor and 30-day customer notice windows, and a guided checklist documents each response step — your firm records every decision.
Record the subcontractors your vendors rely on, the data they access, and how each was identified. A firm-level view flags when the same subcontractor appears under multiple vendors, so concentration is visible.
When you import a contract, AI suggests breach-notification, audit-rights, and subcontractor clauses with the matching excerpt, page, and section. You accept, edit, or dismiss each suggestion — nothing is marked verified on your behalf.
When a vendor returns an assessment, AI compares answers against their attached SOC 2 or security policy, flags discrepancies with cited evidence, and drafts suggested findings for your reviewer to create or dismiss.
Keep review dates, contract notices, expiring evidence, open findings, and assigned tasks visible throughout the vendor lifecycle.
Generate a reproducible PDF and CSV package covering inventory, reviews, findings, contracts, documents, and vendor incidents.
Track every exam request item with an owner and due date, link the vendor records that answer it, and keep a permanent production log of exactly what was sent to examiners.
For broker-dealers, export critical vendors and banks as a Gateway-ready CSV or PDF to support the annual FINRA third-party vendor request — prepared for manual entry, not filed on your behalf.
Recent SEC press releases, rulemaking notices, and risk alerts appear on the Compliance & Regulations page, updated daily with links to the official source.
One master schedule of recurring obligations — filings, reviews, certifications, training, testing — shown alongside every deadline already in your vendor records, with recurring entries that reschedule themselves when marked done.
One-click export of the year's vendor oversight activity — reviews completed, findings raised and resolved, incidents, and recorded decisions, with a linked evidence index — ready for your Rule 206(4)-7 annual program review.
A one-page PDF or spreadsheet of your key service providers — services, risk tier, customer information access, review status, open findings — the summary examiners ask for on day one.
Inside the product
Three of the newest workflows, shown with illustrative sample screens. Every record shown is fictional, and every status is something your firm records — ThirdNexa never labels a vendor compliant or approved.
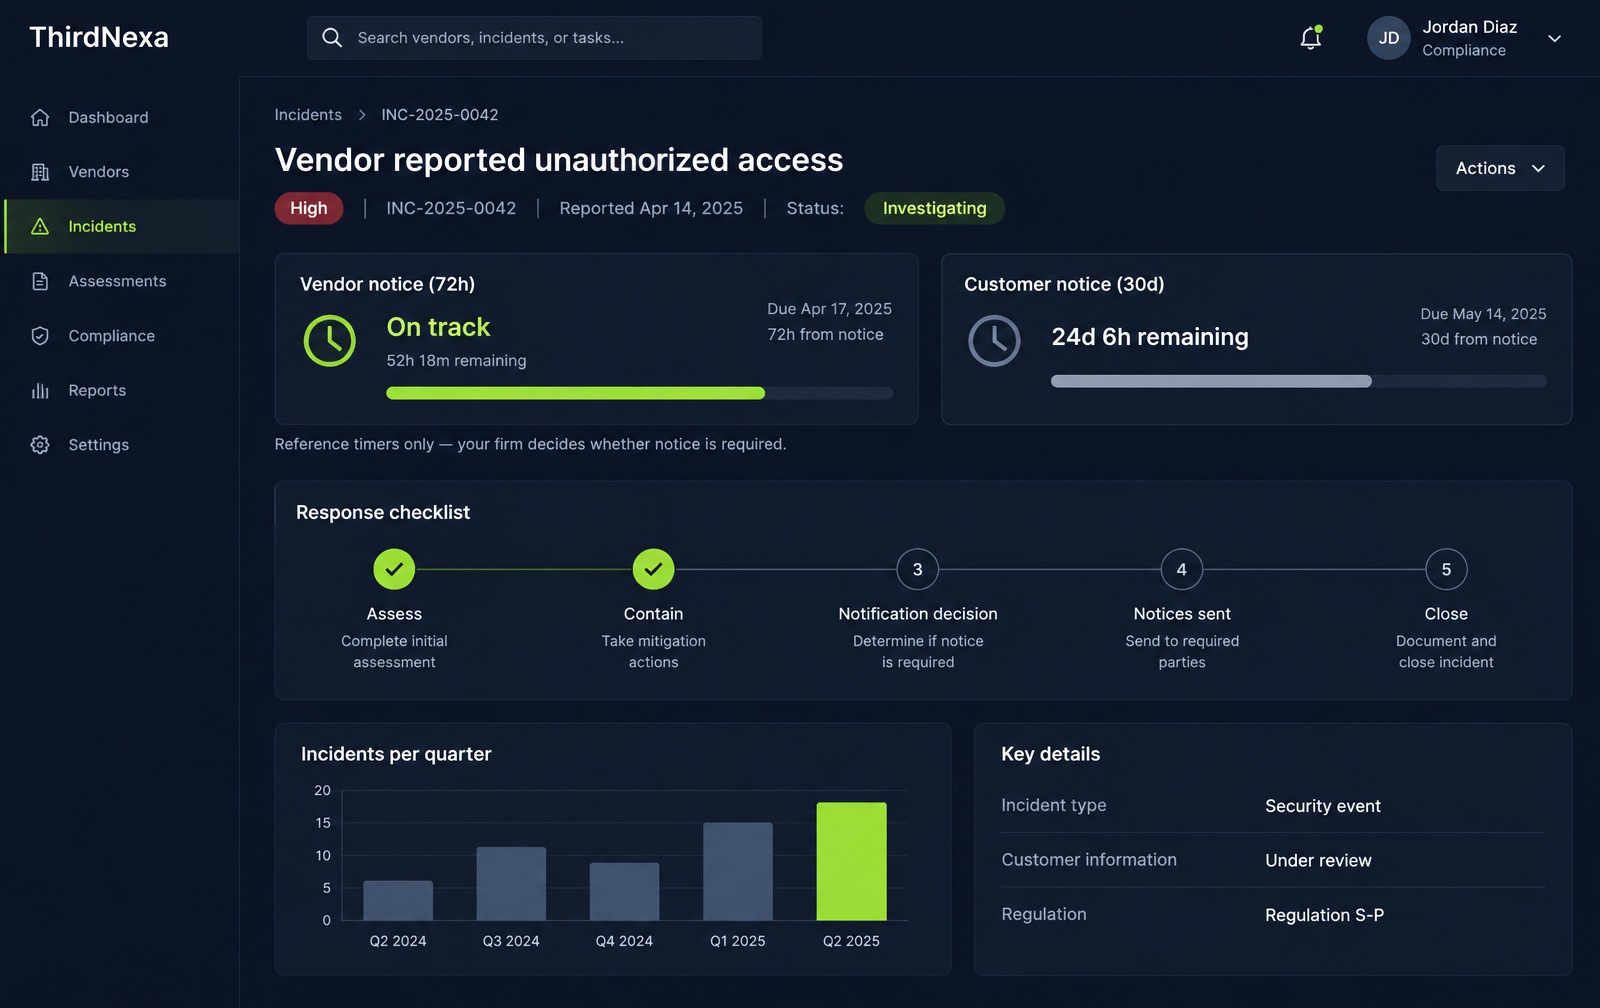
Record breaches, outages, and cyberattacks with severity, root cause, and attachments. Reference timers track the 72-hour vendor and 30-day customer notice windows while a guided checklist documents each step your firm takes.
Illustrative sample screen with fictional data.
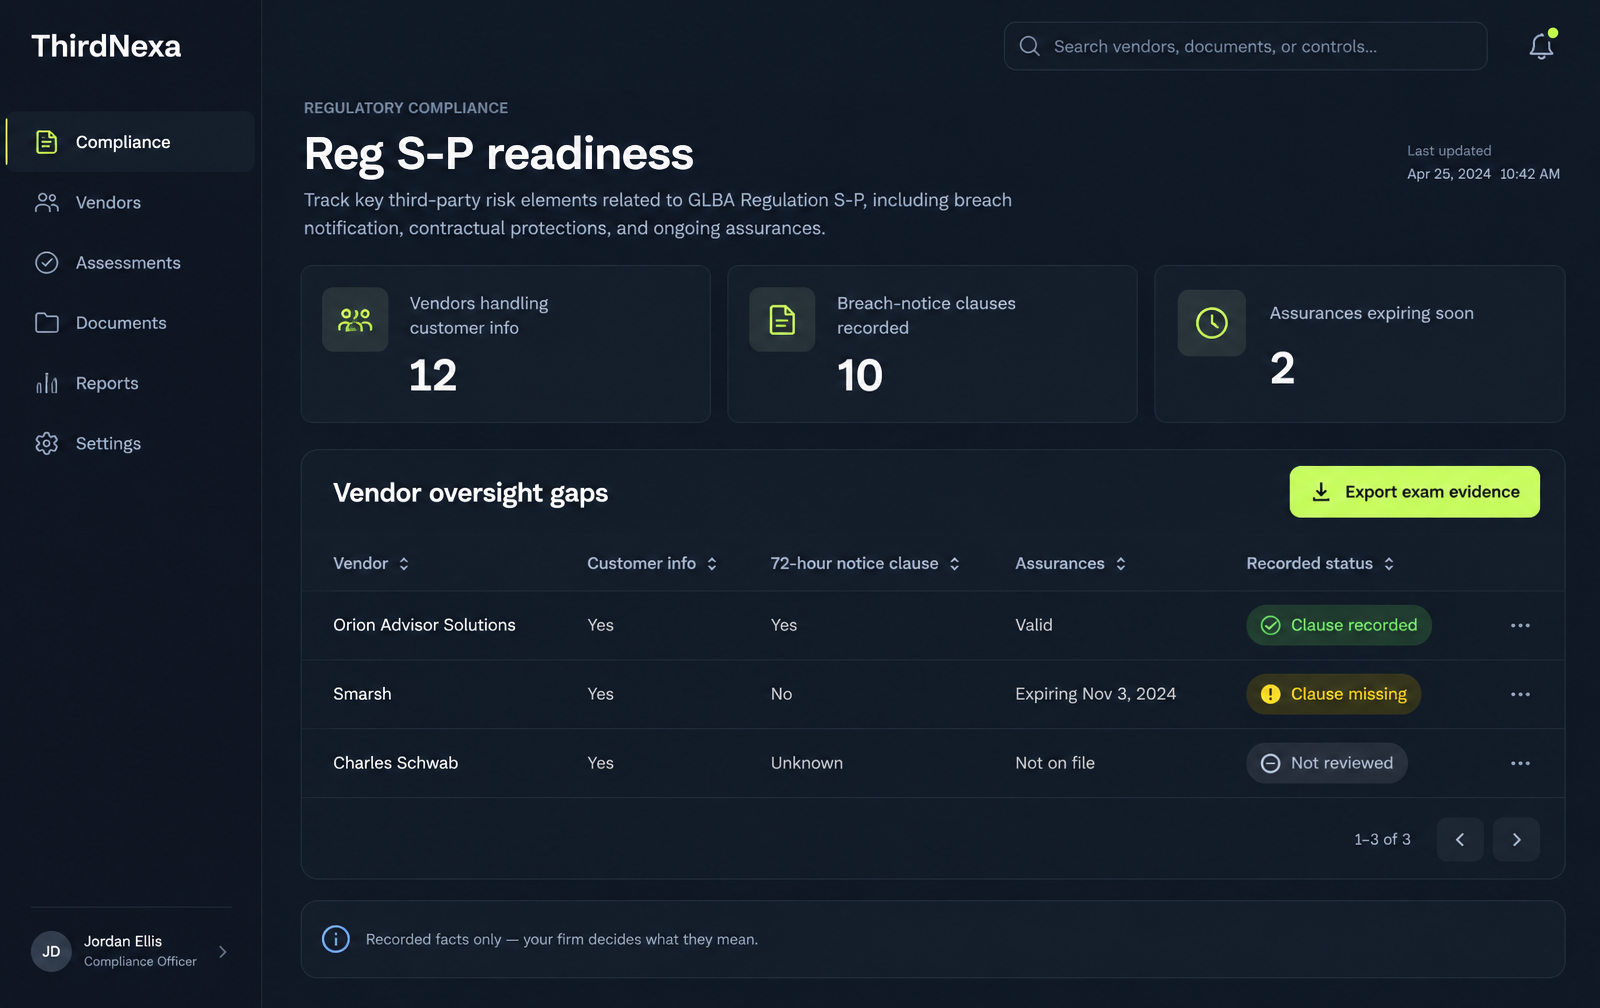
See which vendors handle customer information, whether the breach-notice clause is recorded, and which written assurances are expiring — then export exam evidence per vendor or for the whole firm.
Illustrative sample screen with fictional data.
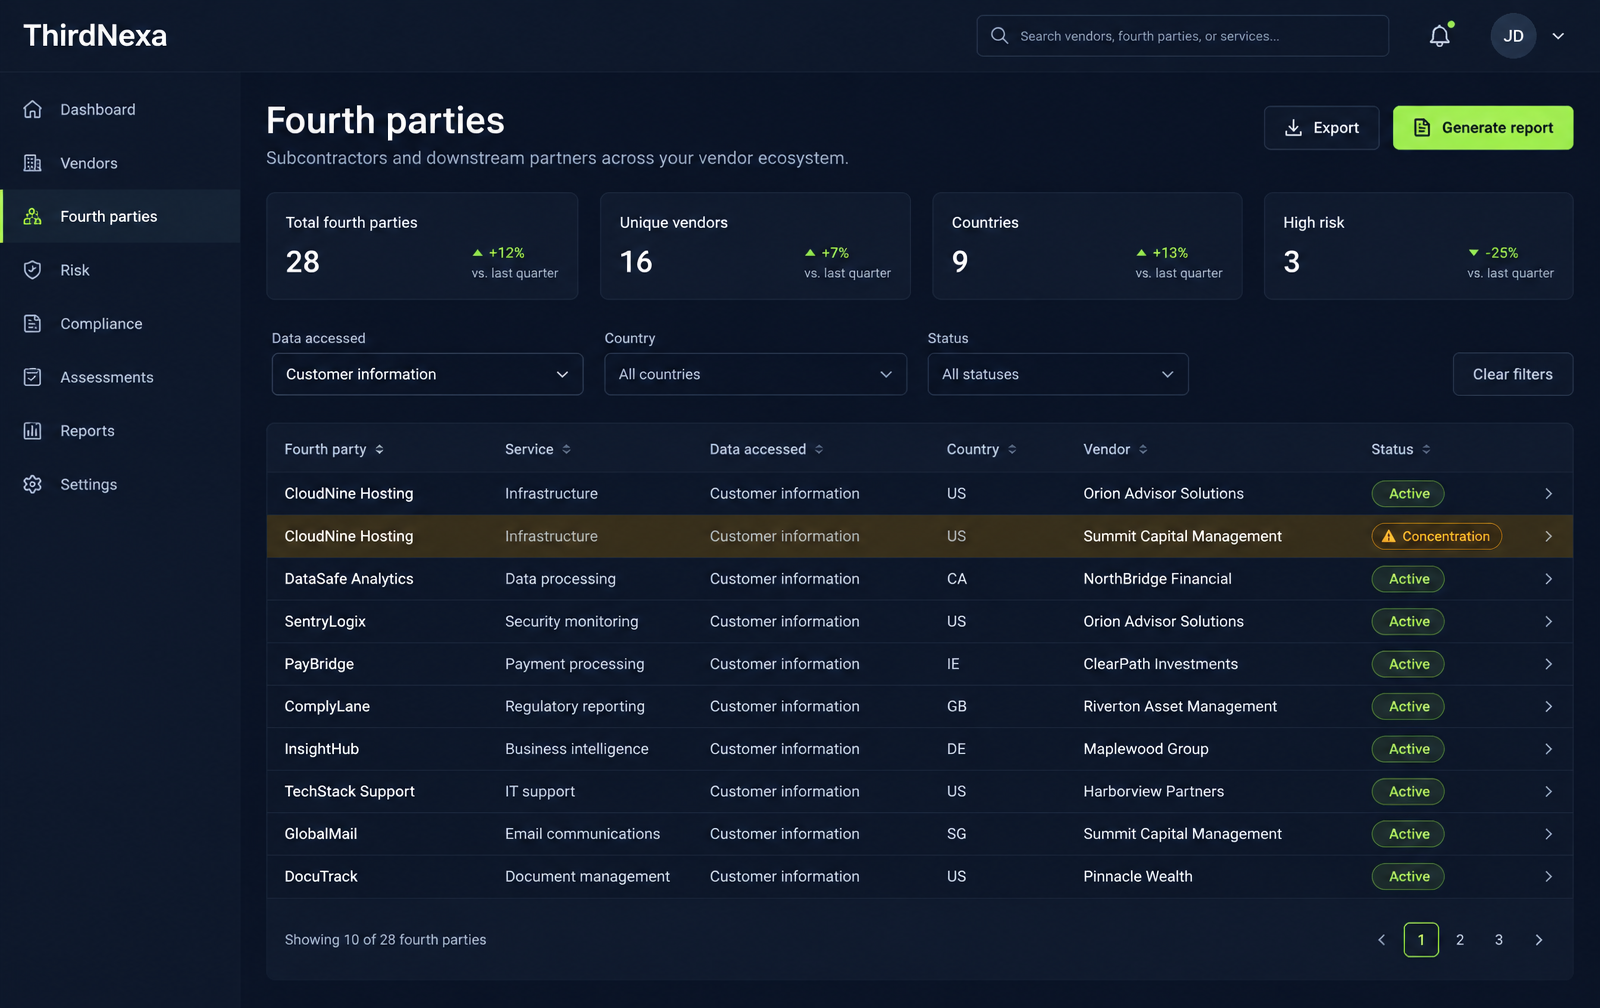
Record the subcontractors behind each vendor, the data they access, and how they were identified. The firm-level view flags when the same fourth party appears under multiple vendors, so concentration is visible.
Illustrative sample screen with fictional data.
Controlled rollout · Staff-enabled per firm
Connect vendor AI inventory, separate risk assessments, questionnaire evidence, reviewer decisions and recorded changes to existing vendor workflows. Signed-in verification is still in progress; availability is controlled separately from your plan.
Explore AI Vendor OversightRegistered investment advisers
For law firms
Outside counsel can organize contract reviews, cited evidence, and supporting records for a client's vendor oversight work in one shared workspace. The client's authorized decision-maker retains every approval — ThirdNexa never treats counsel's work as the client's determination, and law firms are not assumed to share their clients' SEC/FINRA obligations.
Structure contract clause reviews and due diligence evidence for each client engagement.
Every extracted clause and drafted answer links to its source document, page, and quoted passage.
Approvals, risk tiers, and compliance conclusions are recorded only by the client's authorized users.
Works with Claude and ChatGPT
Connect ThirdNexa through the Model Context Protocol (MCP) to search vendors, view risk profiles, check review deadlines, and read open findings and recorded Regulation S-P contract clause statuses.
Ask about the work already in your records
“Which vendor reviews are overdue or due in the next 30 days?”
“Show open findings and remediation details for my vendors.”
“Show recorded Reg S-P contract clause gaps for my vendors.”
Example questions, not customer data or generated answers.
Recorded statuses are not compliance determinations or legal advice. Claude and ChatGPT are third-party services; connector availability depends on their plans and settings. Review their data policies before connecting.
Compliance & Regulations
Review Regulation S-P, Regulation S-ID, Advisers Act Rules 206(4)-7 and 204-2, the Marketing Rule, and FINRA vendor guidance—then see how ThirdNexa supports the documentation work.
See the workflow with your firm or consultancy in mind.